The Multi-License Core for
Regulated Financial Groups
Payments, acquiring and settlement, crypto exchange — each entity under its own license, on one cloud-native core with one ledger. Payment rails, KYC onboarding, need-to-know document access, four-eyes workflows, and multi-currency operations for EMIs, MSBs, and regulated financial groups.
What’s New
Recent additions to the platform. Statuses are stated exactly: built and verified in our development and test environments, or still in development.
Card Acquiring Settlement at Scale
Upload a settlement file, review the validation report, press Process. Control totals are checked before a single document exists; each line then posts through its own workflow, cash settles once per product, and the batch closes with a reconciliation.
AI-Assisted Accounting
Say what happened — "bank fee for the March statement" — and get a draft entry of the right transaction type with its legs filled in. Describe a process and get a draft workflow, checked by the same linter as a hand-made one. AI drafts and checks; it never posts. A person reviews and signs.
Need-to-Know Document Access
Restricted documents open masked. The full view goes to one person, for one document, for a stated reason and a limited time. Secret fields are revealed one at a time; every look and every refusal is recorded. Approvals need a second person, and delegation is single-use.
Web and Mobile Customer Apps
Self-service signup with identity verification, accounts, and payments — on the web and on the phone, with the same features. Payments are approved with passkeys on the web and with a device-bound key in the mobile app, never with SMS codes.
Why Bancorix
Regulated businesses spend 60–80% of early engineering capacity on infrastructure plumbing instead of product differentiation. Bancorix eliminates that trade-off.
Skip 12–24 Months of Build
Launching regulated infrastructure from scratch costs 7-figure budgets and years of compliance debt.
Skip 12–24 Months of Build
Bancorix ships a production-grade ledger, payment rails, KYC onboarding, fee engine, and multi-currency operations out of the box. Launch regulated products in weeks, not years.
Learn More →Compliance by Architecture
Legacy core banking vendors are rigid, slow, and designed for a pre-API world. Point solutions leave compliance gaps between systems.
Compliance by Architecture
FCA, CASS, AML, IFRS, and GDPR requirements are built into every layer — not added as afterthoughts. Tenant isolation is enforced on every query in the data-access layer and covered by a test that fails the build if a tenant-owned entity is added without a filter. Underneath, database row-level security is on for reads and writes, verified in our staging environment: even a query that skipped the filter sees only its own tenant’s rows, and the database refuses any write into another tenant.
Learn More →Configuration Over Code
Adapting to new financial products and regulations usually requires engineering sprints, database migrations, and deployment cycles.
Configuration Over Code
Document schemas and workflows are designed visually in the built-in Schema Studio and Workflow Studio — draft, lint, impact-check, publish. Transaction types, fee structures, and business rules are configuration, not code deployments.
Learn More →Platform Capabilities
Sixteen integrated modules — regulation-aware, need-to-know by default, and configurable without code deployments.
Double-Entry General Ledger
UK/FCA-aligned Chart of Accounts (317 posting accounts) with an in-console editor, full ISO 4217 coverage (155+ currencies) + crypto assets, CASS 6/7 safeguarding, IFRS 9/15/16 support. Every transaction type has a form that defines its legs, so entries arrive balanced and statements read as plain narratives, not "leg 2". Accounts flagged never-negative are guarded at balance write.
Schema-Driven Document Management
Flexible JSON-based document system with 25 predefined document types — KYC, payments (SEPA, FPS, CHAPS, SWIFT), crypto operations, FX, account opening, settlement batches — extensible without code changes. Every document records its origin: console, public API, customer app, or integration.
Configurable Workflow Engine
State-machine-based process automation. All document lifecycle transitions — including every GL posting — go through workflows: no bypass paths, no unaudited state changes. 20 pre-built workflows included.
Need-to-Know Document Access
Fields are classified Normal, PII, or Secret in the schema. Restricted documents open masked by default; the full view needs a role or a time-limited assignment to that one document, revoked automatically. Secret fields such as passport numbers are revealed one at a time with optional MFA step-up. Every full view and every refusal is audited; a privacy mode hides data while sharing a screen.
Four Eyes & Segregation of Duties
Maker-checker is a setting on any workflow transition: the approver must be a different person. A manager can delegate one action on one document to one colleague, once — blocked if it breaks segregation of duties. Manual overrides of system transitions are audited, and each document type declares which channels may create it by hand.
Multi-Rail Payments
SEPA Credit Transfer and SCT Instant, TARGET2, UK Faster Payments and CHAPS, multi-currency accounts with FX, and direct SWIFT on our own BIC — one canonical payment document across all rails, with VoP/CoP pre-payment verification.
Settlement File Import
Card acquiring settlement files arrive as a batch document with its own workflow. A versioned import profile maps the file; it is validated in full before a single document exists, then each line becomes a document that posts through its workflow. Cash settles once per product, and the batch closes with a reconciliation. Measured in our test environment: 200,000-line files at about 75 documents a second, misbalance zero.
KYC & KYB Onboarding
Provider-neutral identity verification (Sumsub first) with embedded WebSDK, self-service signup, corporate KYB with UBO chains, automatic promotion into approval workflows, and scheduled re-sync. Identity documents stay with the provider — Bancorix stores references only.
Fee Calculation Engine
Automated, auditable fee calculation with tiered pricing plans, condition-based rules, manual override support, and a fee simulation dry-run endpoint.
Financial & Regulatory Reporting
Balance Sheet, Profit & Loss, Trial Balance with turnover and revaluation columns, Safeguarding Compliance, and Capital Requirements (FSA061) out of the box — base and multi-currency views, persisted snapshots, and mapping-driven definitions so a new report line is configuration, not code.
FX Rates & Revaluation
Per-tenant FX policy and markup, daily reference feeds from the ECB and the Bank of England, rate snapshots on every converted transaction, realised and unrealised FX posted to the ledger, and a closing-rate balance sheet. Crypto assets are revalued from a market price feed.
Multi-Tenancy with Enforced Tenant Isolation
Tenant isolation is enforced on every query in the data-access layer and covered by a test that fails the build if a tenant-owned entity is added without a filter. Underneath, database row-level security is on for reads and writes, verified in our staging environment: even a query that skipped the filter sees only its own tenant’s rows, and the database refuses any write into another tenant. New tenant provisioned — Chart of Accounts, workflows, admin user — in under 1 minute.
Authentication & Authorization
Roles are granted per tenant — nobody holds a role by default. 18 system roles with group templates, 140+ granular permissions, operator MFA with TOTP, passkeys, email codes, and recovery codes, a per-tenant MFA policy with step-up when switching tenants, account lockout, and a complete audit trail.
Customer Notifications
Template-driven email and SMS through a single notification platform — per-tenant sender identities, delivery receipts and a full delivery ledger, quota throttling, and per-country SMS sender configuration without redeploys.
Configuration & Business Rules
37 system settings, transaction limits scoped to user/account/customer/global, business calendars, payment cut-off and holiday calendars, AML/sanctions toggles — and Schema Studio and Workflow Studio to draft, lint, and publish document types and workflows.
Operations Console
A back-office console redesigned in 2026: dark and light themes that follow the operating system, a command palette (⌘K), status quick filters and keyboard navigation on every list, a peek panel to inspect a document without leaving the list, dashboard charts, reconciliation queues, and integration administration.
Payment Rails & Connectivity
Three payment rails behind one canonical payment document — routed, gated, and reconciled by a dedicated integration engine.
ClearBank Europe — EUR
Virtual IBAN allocation, inbound and outbound payments, recalls and returns, statements — verified end-to-end in our development environment against the provider sandbox.
Observed in sandbox: inbound SEPA posted to the ledger with no manual steps; outbound SCT Instant settled in ~20 seconds; VoP exercised live on payee verification.
ClearBank UK — GBP & Multi-Currency
UK domestic schemes, multi-currency account management, FX request-for-quote, and Confirmation of Payee. Connector code-complete; live verification pending provider-side sandbox activation.
SWIFT — Own BIC
Direct SWIFT connectivity via Alliance Cloud on our own BIC. ISO 20022 CBPR+ messages generated in-house from pinned SR2025 schemas — no vendor message-translation licence. Live traffic pending network onboarding.
The Integration Engine
All external connectivity — payment rails, KYC providers, messaging — runs through one dedicated integration service. The core never talks to a provider directly.
Add a Rail as Configuration
Routing is data: tenant, currency, scheme, instant flag, and amount band select the rail and its capability gates. Adding a rail means reference rows plus a connector — zero core code changes. Demonstrated three times over: payments, KYC, and messaging providers all use the same plug-in model.
Reliable Messaging — At-Least-Once with Idempotent Consumers
Transactional outbox and inbox with deduplication, per-aggregate ordering, retry with backoff, and dead-letter queues with console-driven inspection and replay. Delivery is at-least-once and consumers are idempotent, so a retried message is applied once — the honest form of the guarantee a broker can actually give.
HSM-Backed Signing
Per-tenant credentials in HSM-backed Azure Key Vault. Private keys never leave the vault — operators generate keys and download a CSR from the admin console.
Contract-Governed Events
Canonical event contracts are schema-enforced with golden fixtures and a generated event catalog, so provider drift is caught in CI — not in production.
Rail statuses above are stated exactly: “sandbox-proven” means verified end-to-end in our development environment against the provider sandbox. No production payment traffic yet — production onboarding is scheduled with design partners.
Customer Application
A white-label customer-facing application on top of the core — from self-service signup with identity verification to verified payments.
Self-Service Signup
A customer signs up in the browser — email and phone verification, password, TOTP enrolment, embedded identity verification — and lands in a working account with no operator involvement.
Accounts & Payments
Balances, transactions, fee previews, payee management, and payment initiation across the connected rails — including customer-requested currency accounts approved by operators.
Payee Verification Built In
Verification of Payee runs when a customer adds a payee, with the outcome shown before any money moves and carried into the payment record.
Strong Customer Authentication
PSD2-style dynamic linking — the authorisation is bound to amount, currency, and payee, so changing any of them voids it. WebAuthn passkeys on web; in-app approval signed by a device-bound key on mobile. No SMS codes. Certification and rollout in progress.
Web and Mobile
A web app and a mobile app with the same features — signup, accounts, payments, payee verification, approvals. A financial group can give each licensed entity its own branded app on one platform.
Decoupled and Self-Healing
The apps run on their own database, identity store, and deployment, fed by an asynchronous replicated read model — they never read back-office tables. Strict per-customer event ordering with automatic gap repair reconciles drifted data at login.
The customer web and mobile applications are running in our development environment; the web app was verified end-to-end including hands-free signup against the identity provider sandbox. App store releases and push notifications are on the roadmap.
Platform in Action
End-to-end financial operations — from KYC onboarding to payment settlement — managed from a single back-office console.
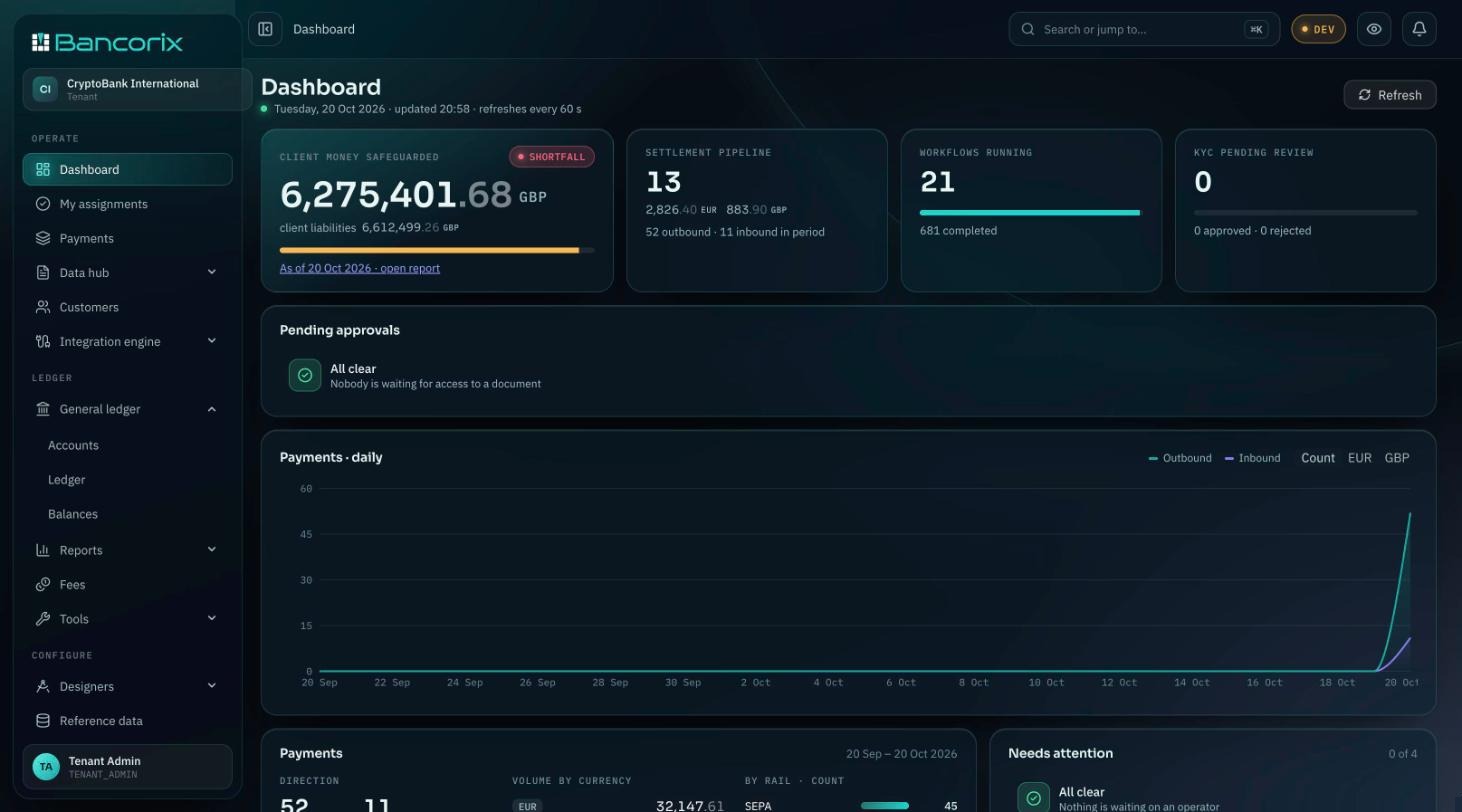
Operations dashboard: client money safeguarded against liabilities, settlement pipeline, running workflows, and daily payment volumes
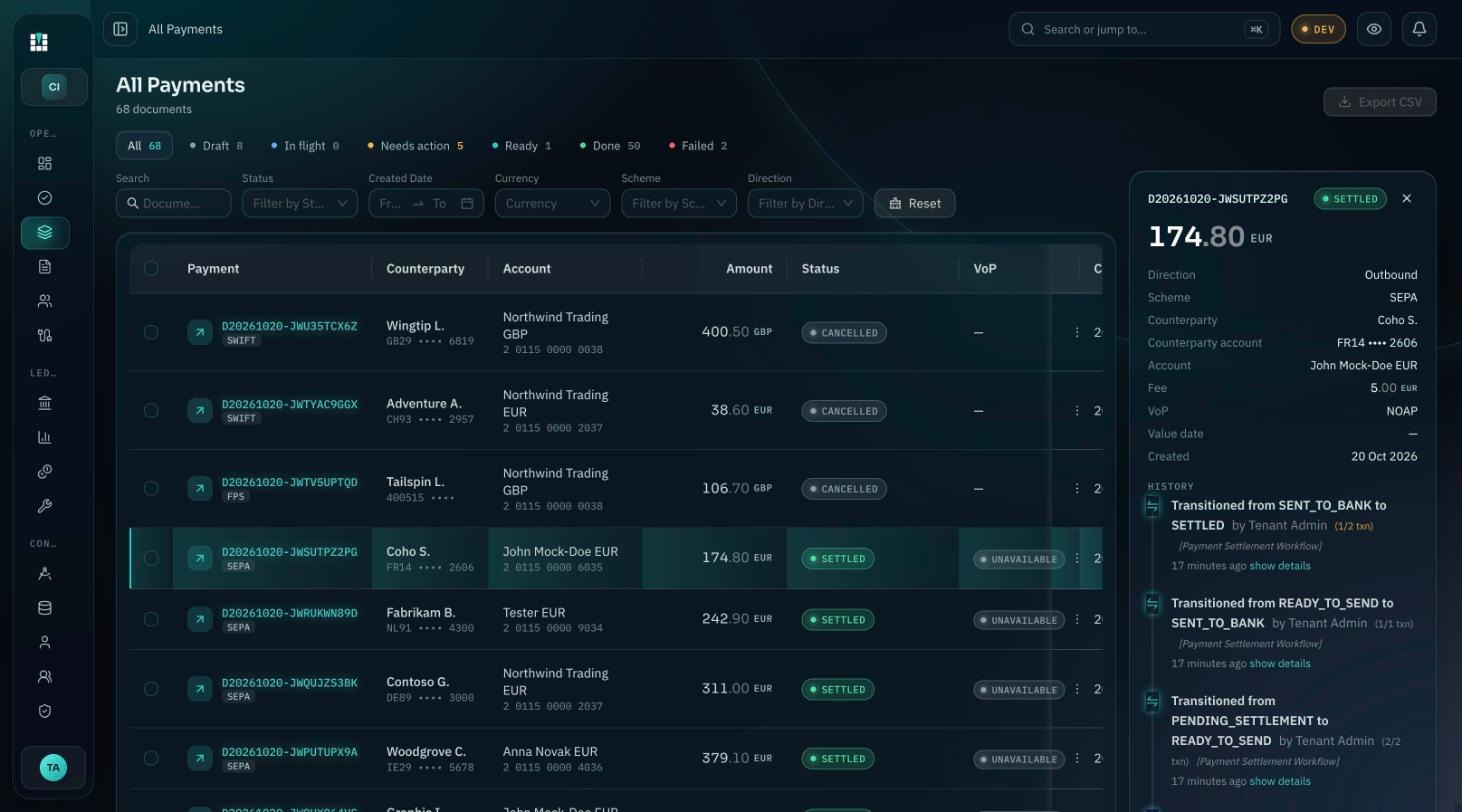
Payments across SEPA, Faster Payments, and SWIFT with status quick filters and a peek panel — details and workflow history without leaving the list
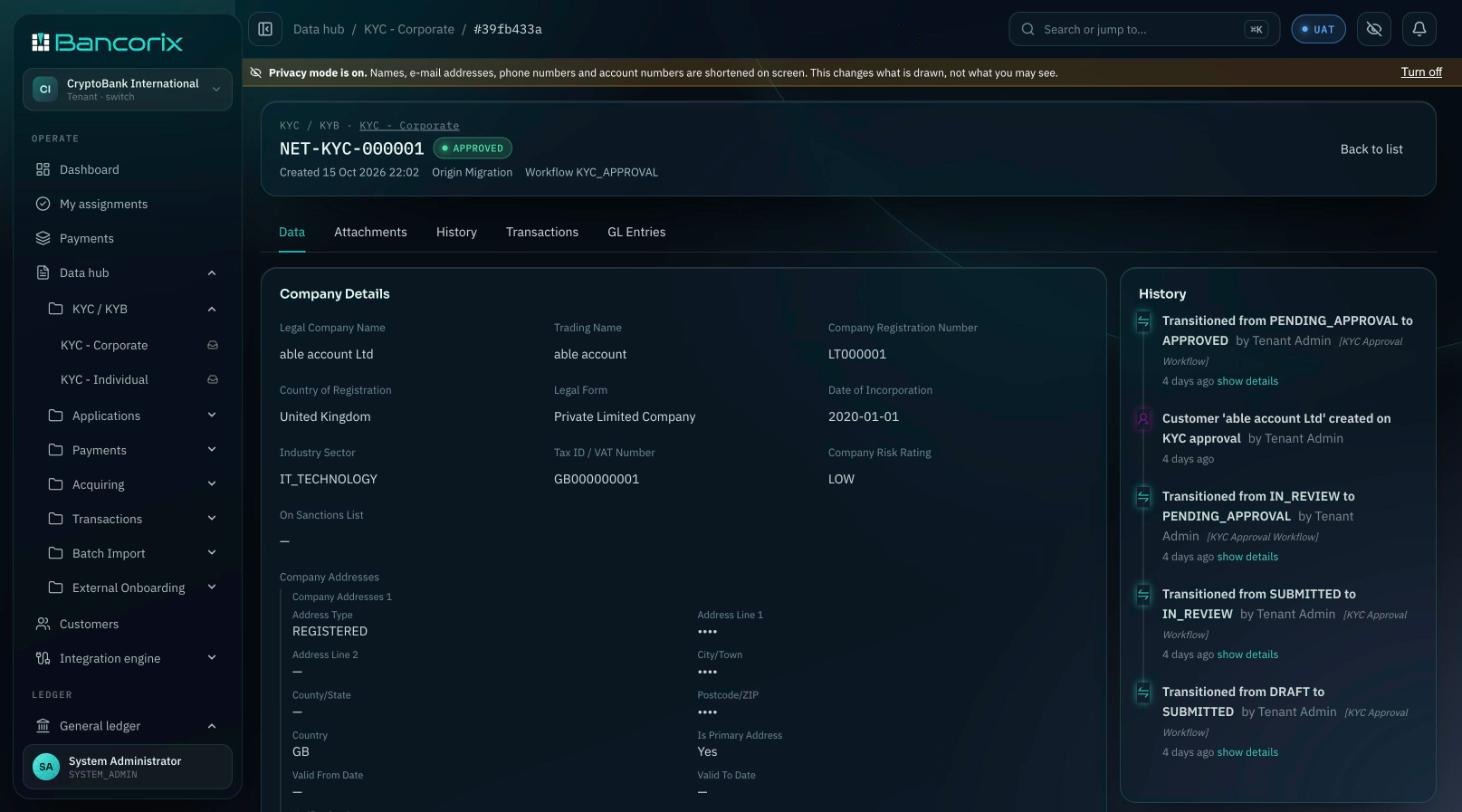
A KYB document in privacy mode for screen sharing, with every workflow transition, actor, and time on record
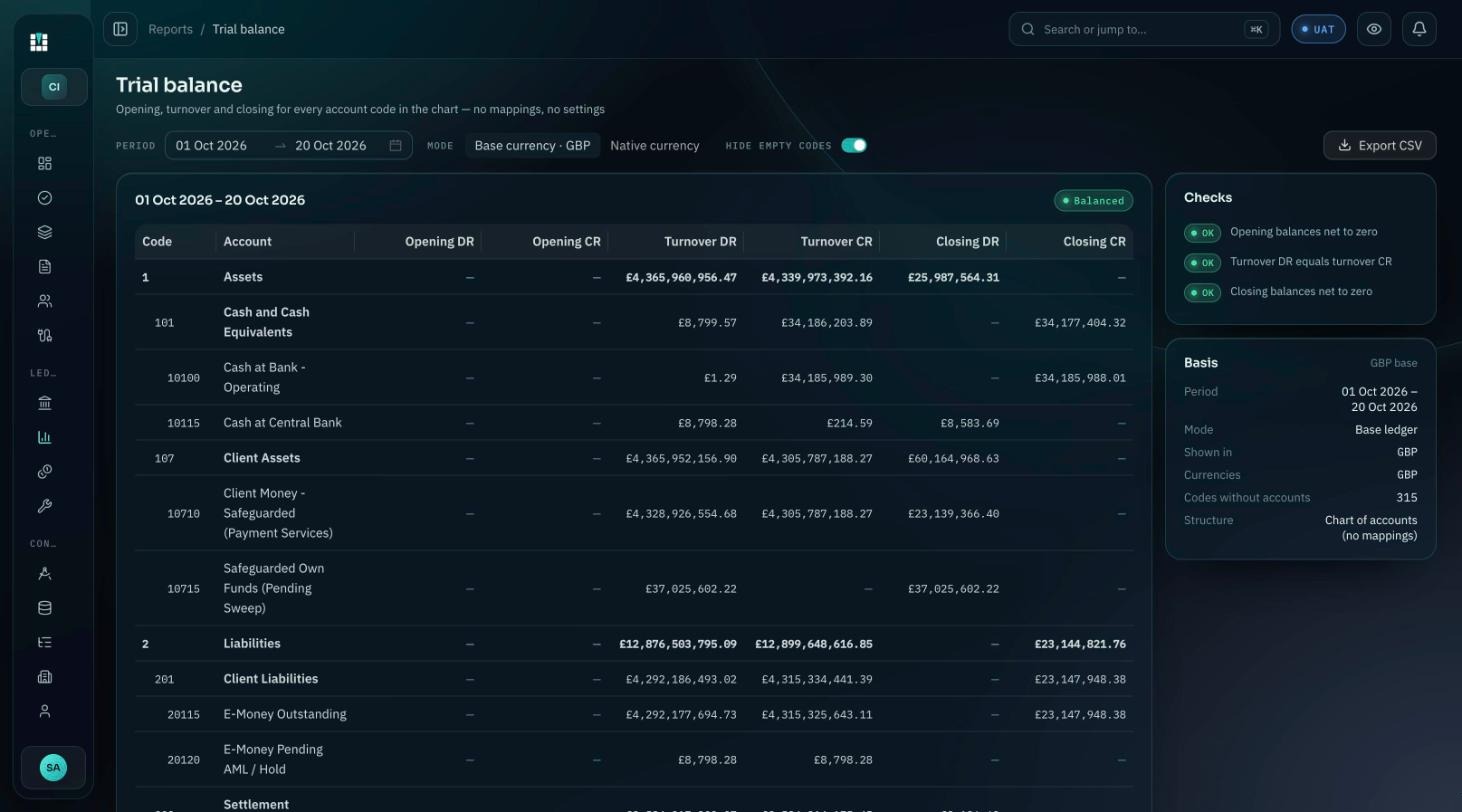
Trial Balance with opening, turnover, and closing per account code, and automatic balance checks
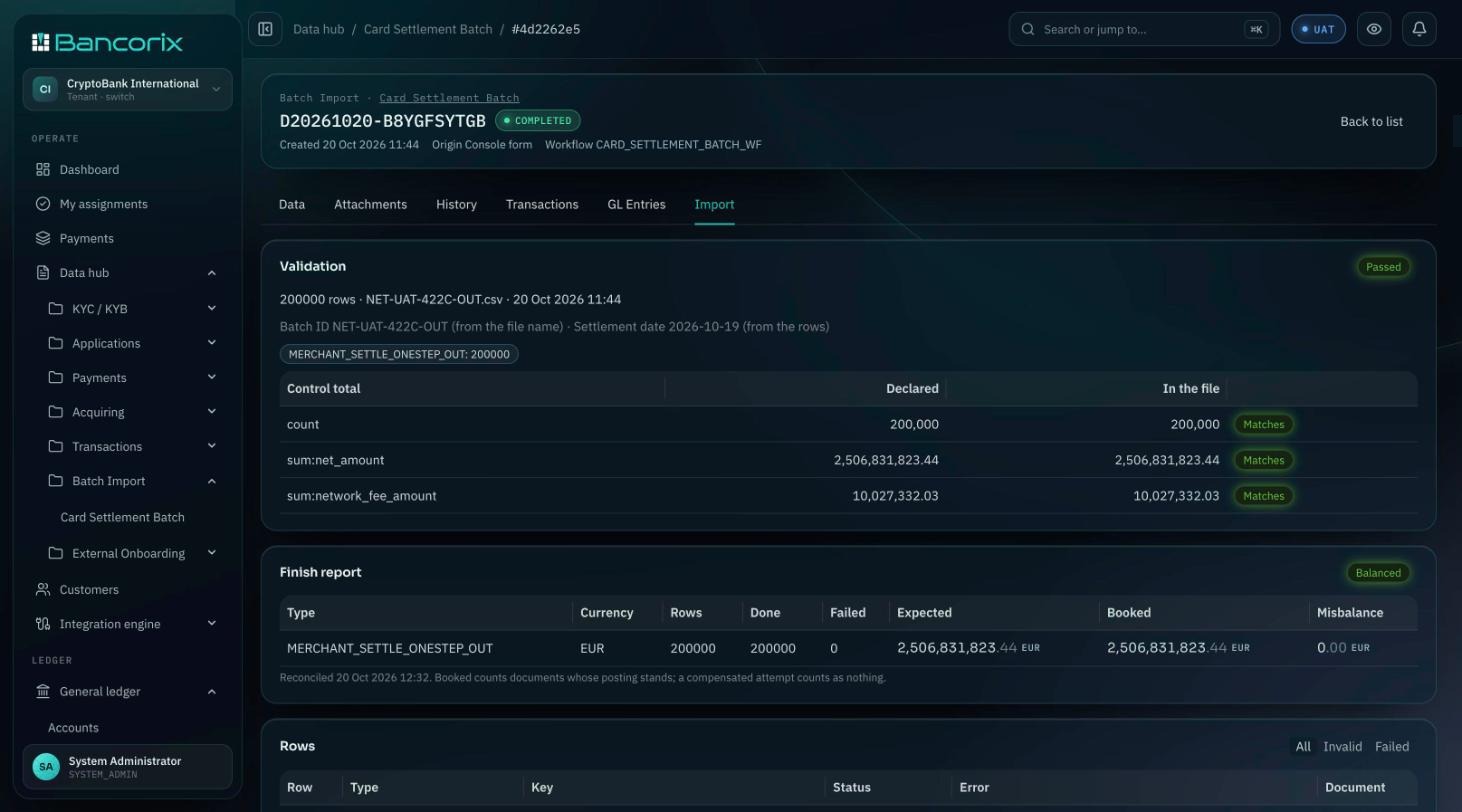
A 200,000-line settlement file: control totals validated before any document is created, every line booked, misbalance zero
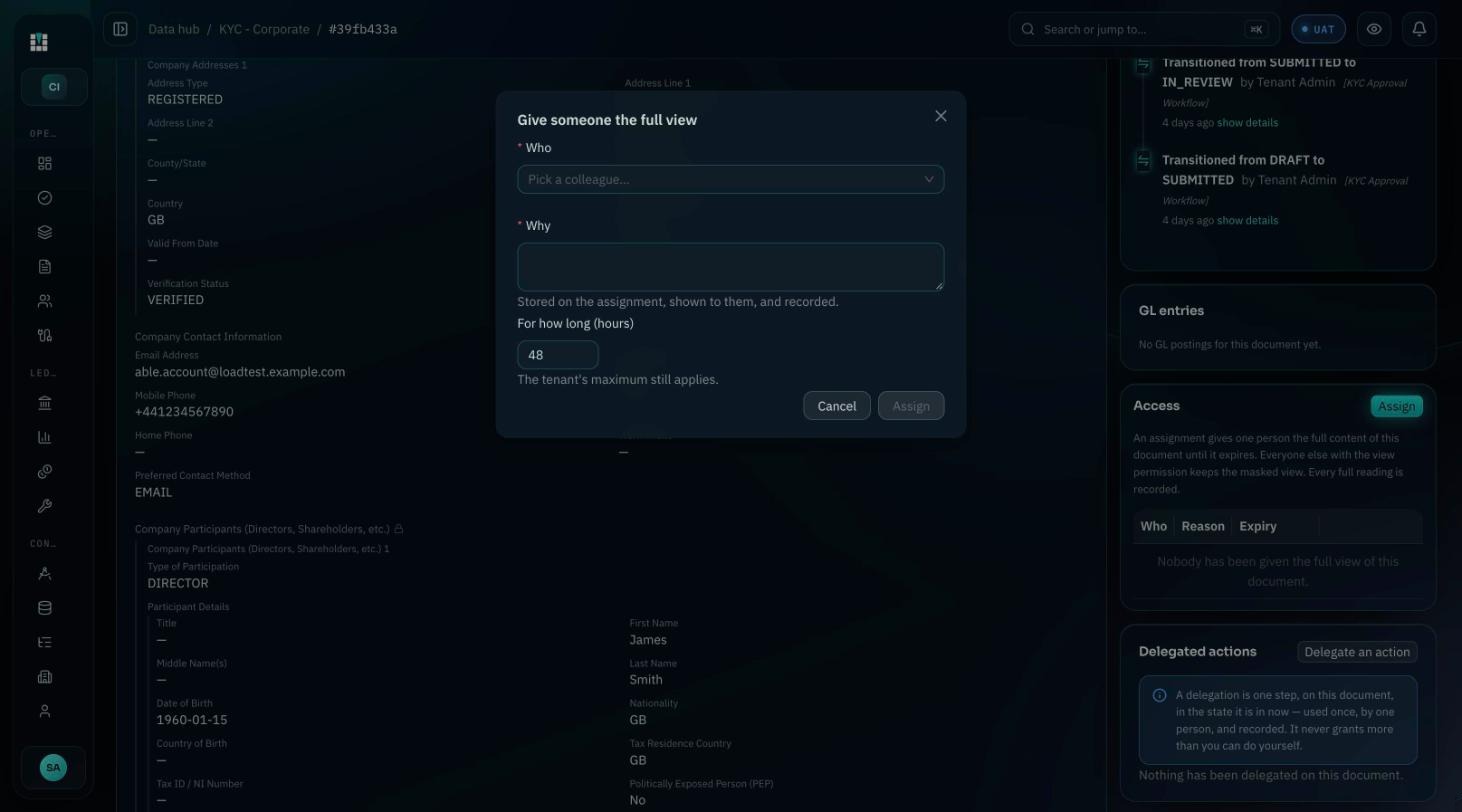
Need-to-know access: one person gets the full view of one document, for a stated reason and a limited time; actions can be delegated once
Platform by the Numbers
A production-grade baseline — not a framework to build on top of. Counts are read from the platform baseline; the estate runs in our development and test environments while we harden for the first production tenant; volumes were measured there.
Regulatory & Compliance Coverage
Compliance is not a bolt-on. Every regulatory requirement is embedded in the architecture from day one.
| Regulation / Standard | What Is Covered |
|---|---|
| FCA / PSD2 | UK FCA-aligned Chart of Accounts, EMI safeguarding accounts, Payment Services Regulations transaction types |
| CASS 6 & 7 | Client money and client asset segregation accounts with matching liabilities, pre-configured and ready to use |
| AML / KYC / KYB | Provider-neutral identity verification (Sumsub integrated) with self-service signup; KYC workflows for individuals, corporates, and partner banks; KYB with recursive UBO chains; sanctions check integration points; AML hold accounts |
| PSD2 SCA | Strong Customer Authentication with dynamic linking — the authorisation is cryptographically bound to amount, currency, and payee: WebAuthn passkeys on web, in-app approval signed by a device-bound key on mobile, and a default-secure exemption policy engine; certification and rollout in progress |
| VoP / CoP | Verification of Payee (SEPA) and Confirmation of Payee (UK) as capability-driven pre-payment gates, selected by routing data per scheme and enforced before funds move |
| IFRS 9 | Three-stage Expected Credit Loss model with separate allowance accounts per stage |
| IFRS 15 | Revenue accounts categorised by service type for contract revenue recognition |
| IFRS 16 | Right-of-Use assets, lease liabilities, depreciation, and interest expense accounts built in |
| GDPR | Tenant-scoped data isolation enforced on every query in the data-access layer, with a coverage test that fails the build if a tenant-owned entity is added without a filter; database row-level security on for reads and writes, verified in our staging environment, so a missed filter still returns only the current tenant’s rows and a cross-tenant write is refused; customer erasure is terminal — once a customer is erased, every write path refuses to recreate their data |
| ISO Standards | ISO 3166-1 full coverage (249 countries with risk flags, FATF grey/black list status, enhanced due diligence flags), ISO 4217 full fiat coverage (155+ currencies, restricted currencies marked non-tradable), ISO 20022 CBPR+ payment messages generated natively from pinned schemas |
| Need-to-Know Access | Data minimisation by design (GDPR Art. 25): fields classified Normal, PII, or Secret in the document schema; restricted documents masked by default; full view by role or by a time-limited assignment to one document; Secret fields revealed one at a time with optional MFA step-up; every full view and every refusal audited |
| Segregation of Duties | Maker-checker on any workflow transition, a different person required to approve; single-use delegation of one action that is blocked when it would break segregation of duties; audited manual overrides of system transitions; per-tenant operator roles with no role held by default; operator MFA with step-up |
| Data Security | Document attachments in private storage with customer-managed keys — no public URLs, single-use time-limited download tokens, rate limits, append-only download audit, and revocable counted access grants for external auditors; KYC biometric documents remain with the identity provider and are never copied into Bancorix |
| Audit Trail | Transactions, workflow transitions and privileged operator actions recorded with actor and timestamp; configuration changes — reference data, tenant settings, document schemas, workflow definitions, notification templates, connector settings — additionally captured field-by-field with old and new values, written in the same database transaction as the change, with secret values redacted |
Who It Is For
Bancorix serves regulated financial services businesses across the full spectrum — from startups to established institutions.
Regulated Financial Groups
One cloud-native core where each entity operates under its own license — EMI, lending, investment, crypto — on a shared platform, replacing the multi-vendor stack financial groups run today.
EMIs, Payment Institutions & Acquirers
Full core banking backbone with FCA-aligned ledger, CASS safeguarding, KYC workflows, fee management, and regulatory reporting — plus card acquiring settlement files of 200,000 lines, reconciled to zero.
Money Service Businesses
Multi-currency operations, payment processing workflows, transaction limit management, and configurable compliance controls across multiple jurisdictions.
FinTech Startups
Skip 12–24 months of infrastructure build. Launch regulated financial products on a production-grade platform and focus on what makes your product unique.
Crypto Exchanges & Brokers
Unified fiat + crypto ledger, wallet management, crypto-fiat exchange operations, and hot/cold storage accounting in a single system.
Embedded Finance Providers
Multi-tenant architecture enables true white-label financial services for downstream clients — each with isolated data, separate workflows, and independent configuration.
Key Differentiators
Ten architectural decisions that separate Bancorix from generic core banking platforms and patchwork integrations.
Built for Multi-License Groups
One cloud-native core where each entity operates under its own license — EMI, lending, investment, crypto — on a shared ledger. License type is a tenant attribute, not a separate vendor stack.
Regulation-Native
FCA Chart of Accounts, CASS safeguarding, AML workflows, IFRS accounting standards, and GDPR data isolation are built into the architecture from the ground up — not added as afterthoughts.
Fiat + Crypto Convergence
Every module — ledger, documents, workflows, fees, reference data — treats cryptocurrency as a first-class asset alongside fiat. Not a crypto extension or a banking retrofit.
Configuration Over Code
Document schemas and workflows are designed visually in the built-in Schema Studio and Workflow Studio — draft, lint, impact analysis, publish, with immutable versioning. Transaction types, fees, and business rules are configuration, not deployments.
Rail-Agnostic Connectivity
Payment rails, KYC providers, and messaging providers plug in through one integration engine. Adding a rail is routing data plus a connector — zero core code changes, demonstrated three times over.
Security by Architecture
Tenant isolation is enforced on every query in the data-access layer and covered by a test that fails the build if a tenant-owned entity is added without a filter. Underneath, database row-level security is on for reads and writes, verified in our staging environment: even a query that skipped the filter sees only its own tenant’s rows, and the database refuses any write into another tenant. Isolation is a build-time invariant, not developer discipline.
Need-to-Know by Default
Access is narrow from the start and widened per document, not per role: a restricted document opens masked, a full view needs an assignment that expires, and every look is on record. Approvals need a second person, and delegation cannot break segregation of duties.
Workflow-First Integrity
All document state changes go through the workflow engine. No bypass paths, no dual-state tracking. Every transition is logged, permission-checked, and auditable.
Production-Grade Baseline
20 pre-built workflows, 150+ transaction types, 317 GL posting accounts, full ISO 4217 + ISO 3166-1 coverage, automated tenant provisioning, dual API surface. Ships configured to operate, not as a framework to build on.
Dual API Architecture
Core API for external integrations and partner connectivity; Console BFF for back-office operations. Each evolves independently without breaking the other.
Ready to Evaluate?
Explore the live API documentation or request a hands-on demo with your specific regulatory context.
Roadmap — Coming Soon
The following capabilities are on the Bancorix roadmap, extending the platform into a fully connected financial services ecosystem. Not yet available — listed for planning and partnership purposes.
Card Issuing & Processing
White-label card issuing via Marqeta, Thredd, Moorwand — physical and virtual cards, 3D Secure, Apple/Google Pay tokenisation.
Open Banking (PSD2 / Open Banking UK)
Account Information Services (AIS) and Payment Initiation Services (PIS) with VRP, consent management, and multi-bank dashboard.
Transaction Monitoring & Sanctions Screening
Rules-based AML screening, automated sanctions and PEP list checking, ML-powered anomaly detection hooks, case management, and SAR filing.
Custom Report Builder & Regulatory Returns
Balance Sheet, P&L, Safeguarding, and FSA061 reports ship today. Coming next: a custom report builder with PDF/CSV export and automated FCA regulatory return filing.
App Store Releases & Push Notifications
The mobile app already matches the web app on features. Next: App Store and Google Play releases and push notification delivery.
Open App Source for Clients
The source code of the web and mobile customer apps, opened to clients: publish under your own name, in the app stores too, and restyle to your brand. Authentication, payment signing, and the App API stay on the platform side.
AI-Assisted Accounting
Describe what happened in plain words and get a draft entry of the right transaction type with its legs filled in; describe a process and get a draft workflow. AI drafts and checks — it never posts. A person reviews and signs.
Digital Asset Custody
Stablecoin and crypto custody through Fireblocks as a rail of the integration engine, with on-chain document workflows and reconciliation on the same ledger as fiat.
Bring Your Own Ledger
Run the Bancorix document, workflow, and compliance layer on top of an external ledger kernel — vendor abstraction with account mapping to the FCA chart of accounts and continuous reconciliation.
API Documentation
API-first architecture with full OpenAPI 3.0 specifications, interactive Swagger UI, and Postman collection. Build integrations against a well-defined, versioned contract.
Core API
External integrations & partner connectivity
RESTful API for external systems, partner integrations, and programmatic access to all platform capabilities. OpenAPI 3.0 specification with full Swagger UI.
Console API (BFF)
Back-office operations & administration
Dedicated back-office API surface for the operations console. Evolves independently from the Core API without breaking partner integrations.
Postman Collection
A complete Postman collection with pre-configured environments is available for rapid integration testing. Request access via ask@paydevops.com.
API Access
API access is tenant-scoped and requires a Bancorix subscription. Contact us to provision a sandbox environment for technical evaluation.
Full API Guide
Detailed integration guides, authentication flows, webhook setup, and code samples available in the API Guide.
Get In Touch
For demo requests, partnership inquiries, technical evaluation, or any questions about Bancorix.
Phone
Website
Location
Lisbon, Portugal
Company
Request a Demo
See Bancorix in action with your specific regulatory context — EMI, Payment Institution, MSB, or Crypto Exchange. We walk through live workflows, the GL, fee engine, and console operations tailored to your use case.
Request a DemoTechnical EvaluationSandbox Access
We can provision a sandbox environment with pre-loaded data for hands-on technical evaluation. Contact us to get started.